Exhaustive Compliance Mapping
PAM-Pro is not just a security tool; it is a regulatory enforcement engine. Below is the mapping of our JIT architecture to specific global compliance controls.
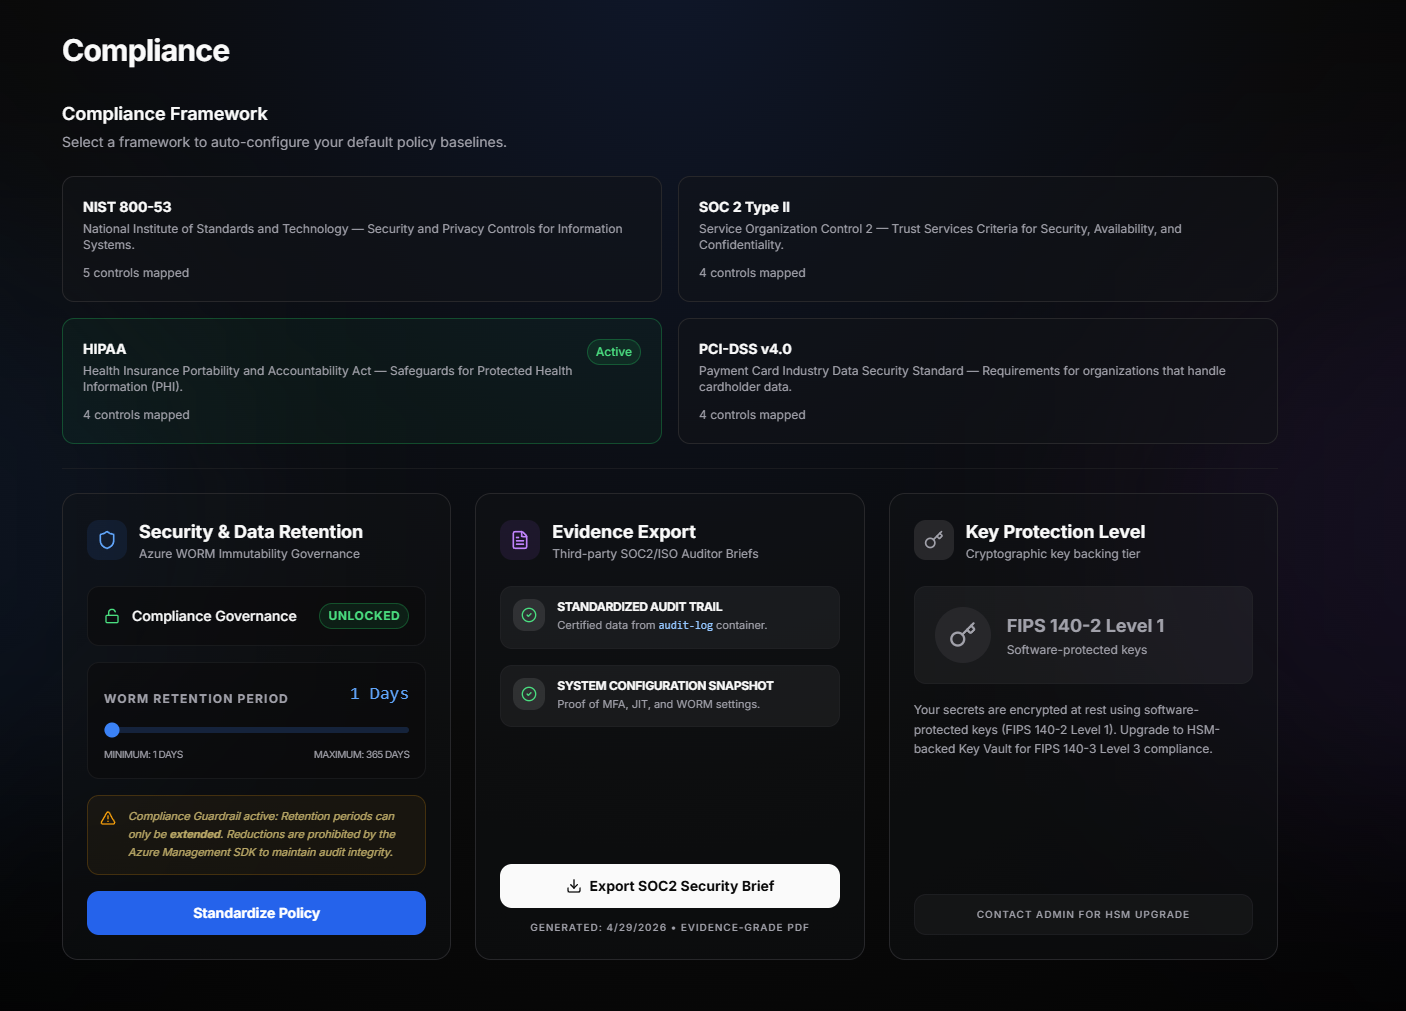
HIPAA Security Rule
The Security Rule requires covered entities to implement technical policies and procedures for electronic information systems that maintain PHI to allow access only to those persons or software programs that have been granted access rights.
SOC 2 Type II Ready
Trust Services Criteria for Security and Availability require that the entity restricts logical access to confidential information to authorized users to prevent unauthorized use.
NIST SP 800-53 Rev. 5
Federal information systems mandate the principle of Least Privilege (AC-6), requiring that users are granted only the access necessary to perform their duties.
HITRUST CSF
The Common Security Framework (CSF) mandates rigorous user management and access control systems for safeguarding health and financial data.
GDPR Data Protection
Article 32 requires technical and organizational measures to ensure a level of security appropriate to the risk, including the ability to ensure persistent confidentiality and integrity.
ISO/IEC 27001:2022
ISO/IEC 27001 Annex A controls mandate that the allocation and use of privileged access rights shall be restricted and managed.