Answer your insurance questionnaire with evidence, not attestations.
Huntoso PAM-Pro reads your Microsoft Entra ID tenant and produces dated, exportable proof that privileged access is controlled: standing admin rights, MFA verified on every credential checkout, session records. No agents. No servers. About ten minutes.
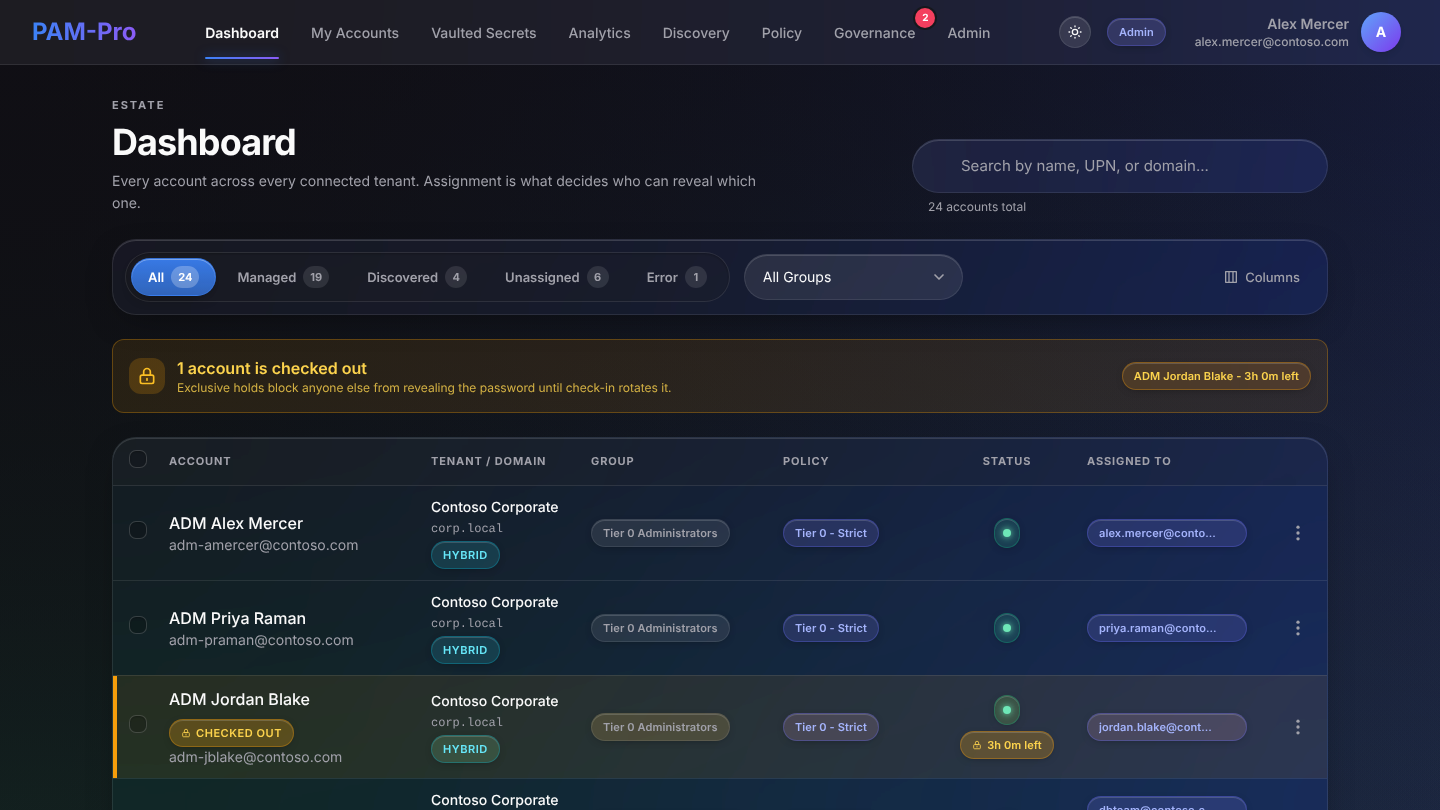
How many Global Admins are in your tenant right now?
Microsoft's own guidance says fewer than five. Most organizations cannot answer without opening the portal and counting. Your underwriter asks a version of that question every renewal, and a yes/no checkbox is no longer the answer they accept.
"Do any accounts hold standing privileged access?"
A dated inventory of every privileged account in the tenant, including the unmanaged ones nobody remembered creating, with standing rights removed and just-in-time checkout in their place.
"Is MFA enforced on every privileged elevation?"
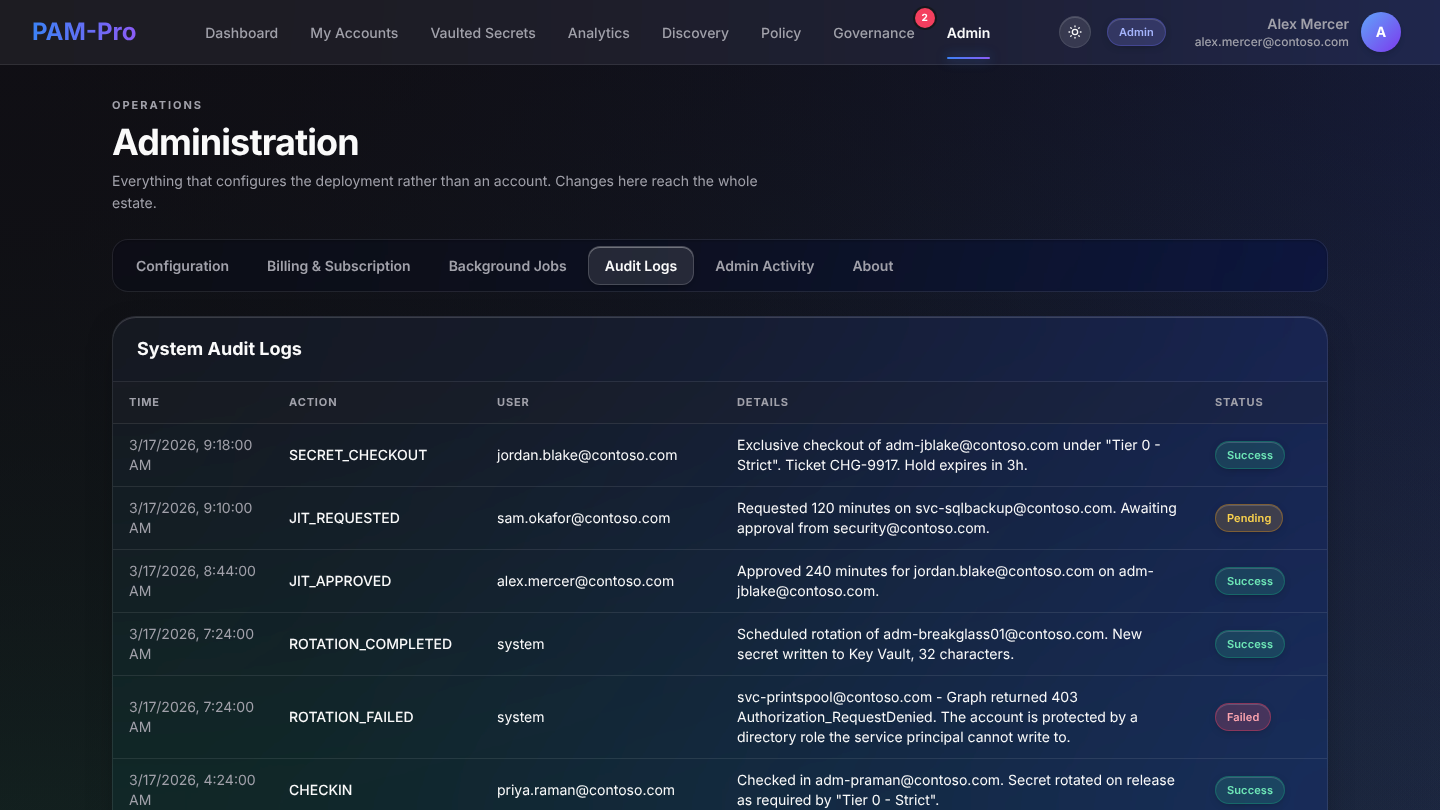
Per-checkout records showing whether the sign-in that released the credential was MFA-backed, read from the token's authentication-method claim. Checkouts arriving without it are refused and logged. Measured evidence, not a screenshot of a policy that may or may not apply.
"Can you produce records of privileged activity?"
Write-once, read-many checkout and session history covering who elevated, to what, when, and for how long, exportable for the renewal file and forwarded live to Sentinel or Splunk.
The evidence pack
One dated export you attach to a renewal application or hand to an auditor. Generated from your live tenant, not typed into a form.
Why this is different from a policy screenshot
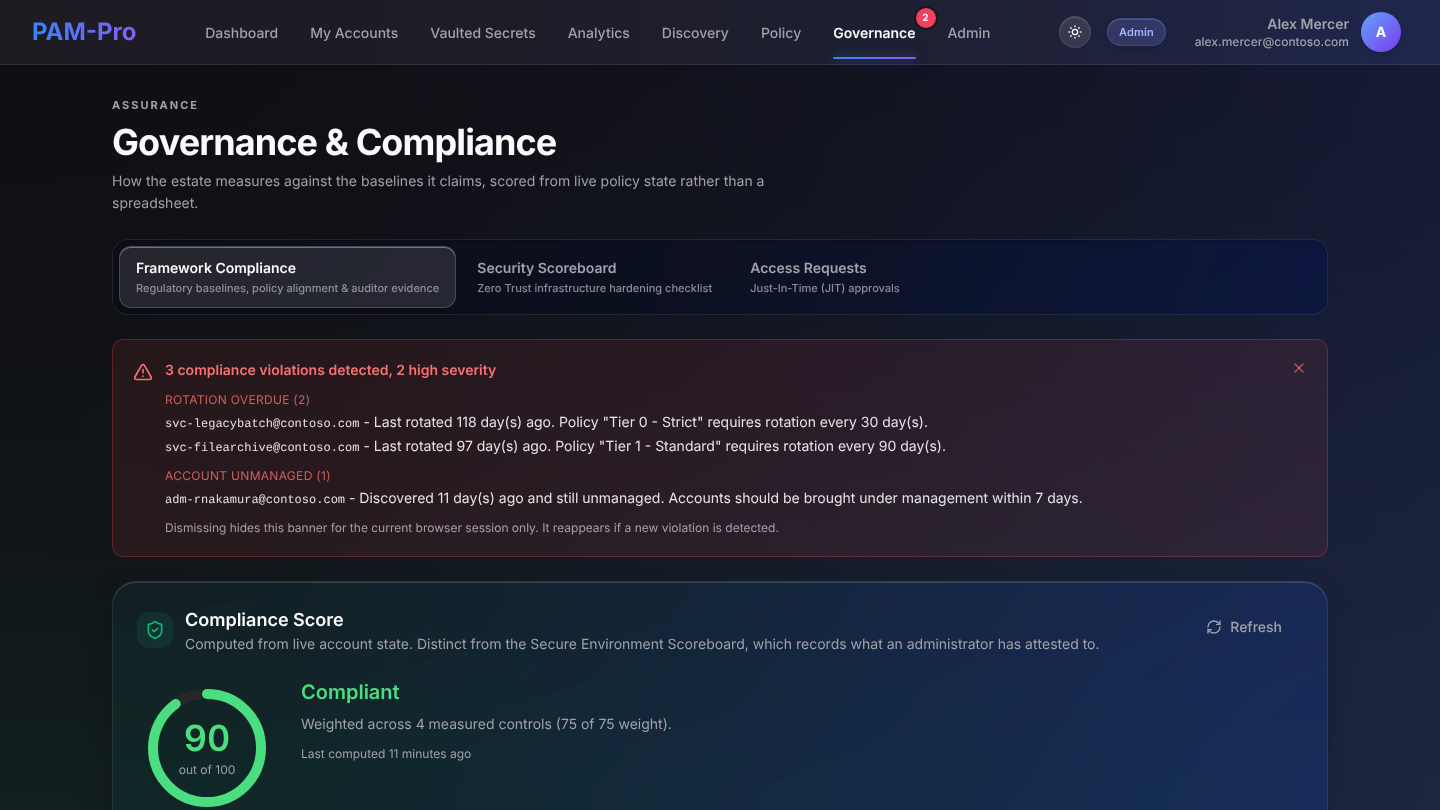
A configuration screenshot proves a setting existed on the day you took it. The evidence pack is generated from what actually happened in your tenant: the accounts that exist, the elevations that occurred, and whether each one was released to an MFA-backed sign-in. That is the difference between an attestation and proof.
The first pass is discovery
The trial is fully featured from day one, but PAM-Pro starts by inventorying. It shows you your own numbers before you change a single permission, and nothing in your tenant changes until you act. Most teams find accounts they did not know were privileged in the first ten minutes.
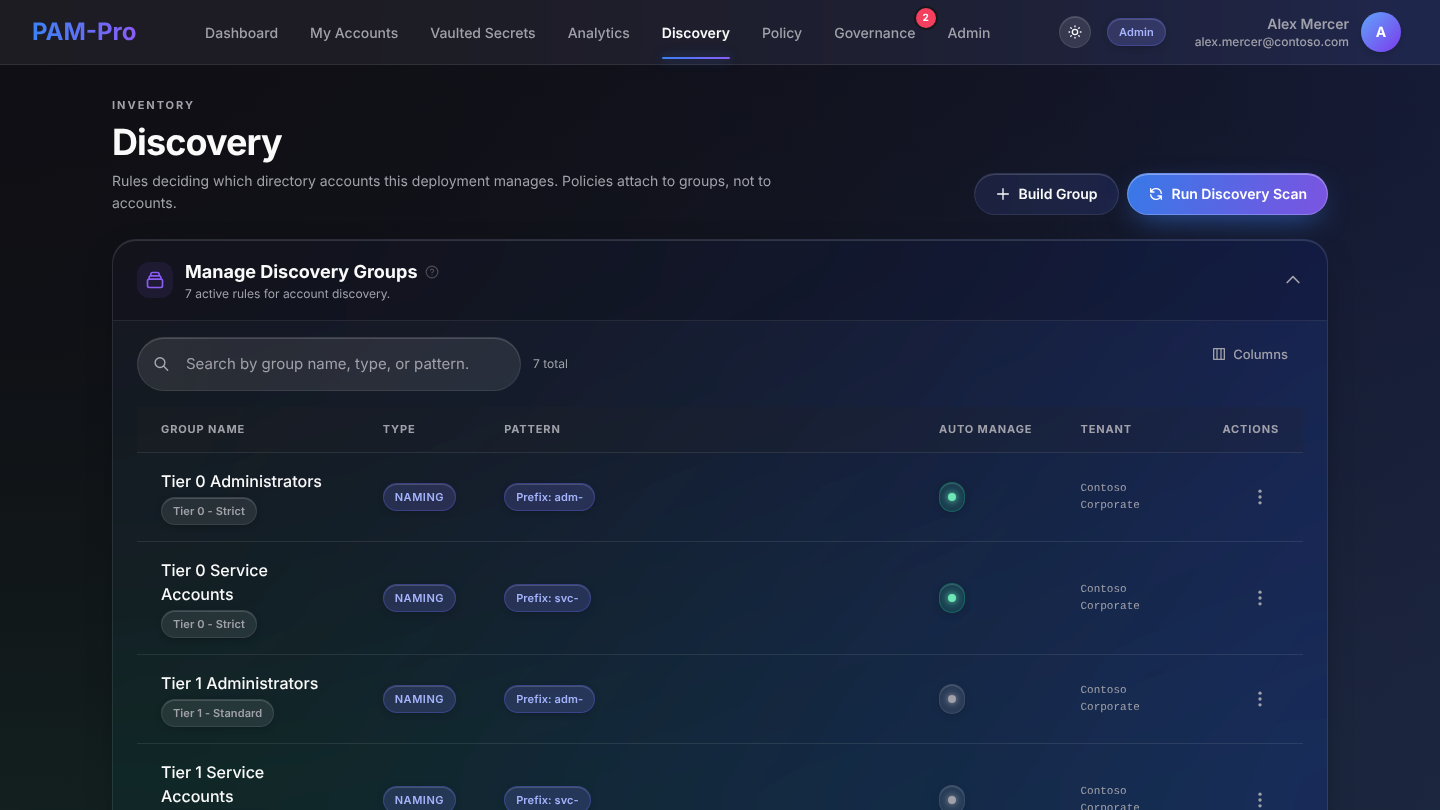
Module 01: Automated Account Discovery
PAM-Pro automatically scans your Microsoft Entra ID tenant using configured Discovery Groups (matching prefix/postfix rules like adm-*). Unmanaged accounts are discovered and promoted to Managed Accounts subject to policy governance.
How it works
No procurement cycle, no professional services engagement, no pilot environment to stand up.
Consent, do not install
Grant consent to the Huntoso enterprise application in your Entra ID tenant. Nothing is installed and no inbound firewall change is required.
See your real numbers
PAM-Pro inventories every privileged account through the Microsoft Graph API, including the unmanaged accounts that fail access reviews and get claims denied.
Retire standing access
When you are ready, switch standing rights to just-in-time checkout gated on MFA, a one-hour expiry, and automatic credential rotation on check-in.
Hand over the proof
Generate the dated evidence pack for the renewal file or the auditor, and forward the same records continuously to your SIEM.
See PAM-Pro in Action
A two-minute tour of the real product: reveal a credential with a reason and a ticket, request time-boxed access, review vaulted secrets, test a policy, and watch the live compliance score.
There is nothing to install
Legacy PAM takes months because it ships kernel agents, jump servers and a vault appliance you have to run. PAM-Pro governs your tenant through the Microsoft APIs it already exposes, so there is no deployment project between you and the evidence.
Zero Workstation Agents
Nothing installed on user machines. Governed 100% via official Microsoft Entra ID APIs.
10-Minute Setup
Register the Huntoso enterprise application in your Azure tenant and start governing immediately.
Flat $20 / User / Month
Transparent flat pricing with a 20-seat minimum. Zero hidden add-ons or audit tier fees.
You Own The Encryption Keys
Secrets are encrypted with your Tenant Root Encryption Key (TRK) in your own Azure Key Vault.
The 3-Year Reality for 30 Administrators
Legacy sales reps quote low licenses then add $40k-$60k in professional services and server VMs. Huntoso eliminates the overhead completely.
Three ways teams arrive here
Small and mid-sized organizations running Microsoft Entra ID, and the partners who manage them.
Continuous Audit & Compliance
Satisfy auditor requirements for HIPAA 164.312, SOC 2 CC6.1, and NIST 800-53 without paying for expensive enterprise audit add-on modules.
- ✓ Immutable Write-Once, Read-Many (WORM) audit storage lock
- ✓ Real-time SIEM forwarding to Microsoft Sentinel and Splunk
- ✓ Automated 1-click evidence report generation
Cyber Insurance Accelerator
Your carrier stopped accepting yes/no answers on privileged access and MFA. Produce the proof you need to qualify for and keep coverage, in an afternoon rather than a quarter.
- ✓ Pre-mapped answers for Marsh, Travelers, and Beazley questionnaires
- ✓ Credential checkout refused unless the session carries MFA
- ✓ Eliminates unmanaged accounts before carrier inspection
Multi-Tenant Client Fleets
Govern privileged access across every client tenant from one place, and hand each client their own dated evidence pack at renewal without a per-client deployment project.
- ✓ Per-tenant encryption keys held in each client's own Key Vault
- ✓ No agent rollout or server build per client
- ✓ Separate, exportable evidence per tenant
The price is on the website
No custom quote, no discovery call before you can see a number, no add-on module for the audit reports.
Up to 20 managed accounts: $3,000 paid yearly, or $265 billed monthly. Beyond 20 accounts: $20 per account per month.
Where the legacy money goes
Most of a legacy PAM budget is spent standing the thing up. There is no implementation project here, so that line is zero - which is why the evidence arrives in minutes instead of quarters. Figures below assume a 20 to 50 account environment.
| Platform | 3-Year Licensing | Implementation Services | VM Infrastructure | Deployment Time | Total 3-Yr TCO |
|---|---|---|---|---|---|
| Huntoso PAM Pro | $9,000 - $22,500 | $0 (Self-Serve) | $0 (Cloud Native) | 10 Minutes | $9,000 - $22,500 |
| CyberArk Enterprise | $125,000+ | $60,000 | $15,000 | 3 - 6 Months | $200,000+ |
| BeyondTrust Privilege | $80,000+ | $40,000 | $10,000 | 2 - 4 Months | $130,000+ |
| Delinea Secret Server | $50,000+ | $25,000 | $5,000 | 4 - 8 Weeks | $80,000+ |
Public status page
Component-level health and historical uptime for the API, authentication, vault operations and storage, published at status.huntoso.ai.
Zero-secret exchange
Your credentials are encrypted under a Tenant Root Key held in your own Azure Key Vault. We never take custody of the master key.
Published release notes
Every release is documented in public, including the security work. You can read what changed before you decide to trust it.
Explore The Lab
Beyond privileged access management, Huntoso builds open blueprints for architecture governance, agentic authorship, and cloud financial reconciliation.
Visit The Lab →Prefer to talk first?
You do not need to. The trial is self-serve and fully featured for 14 days. Signup runs through Stripe Checkout, so a card is collected up front, but nothing is charged for 14 days and you can cancel before they are up. If you would rather have a conversation about your tenant, a private POC, or an MSP rollout, this reaches an engineer.