The MFA Checkbox That's Quietly Wrong
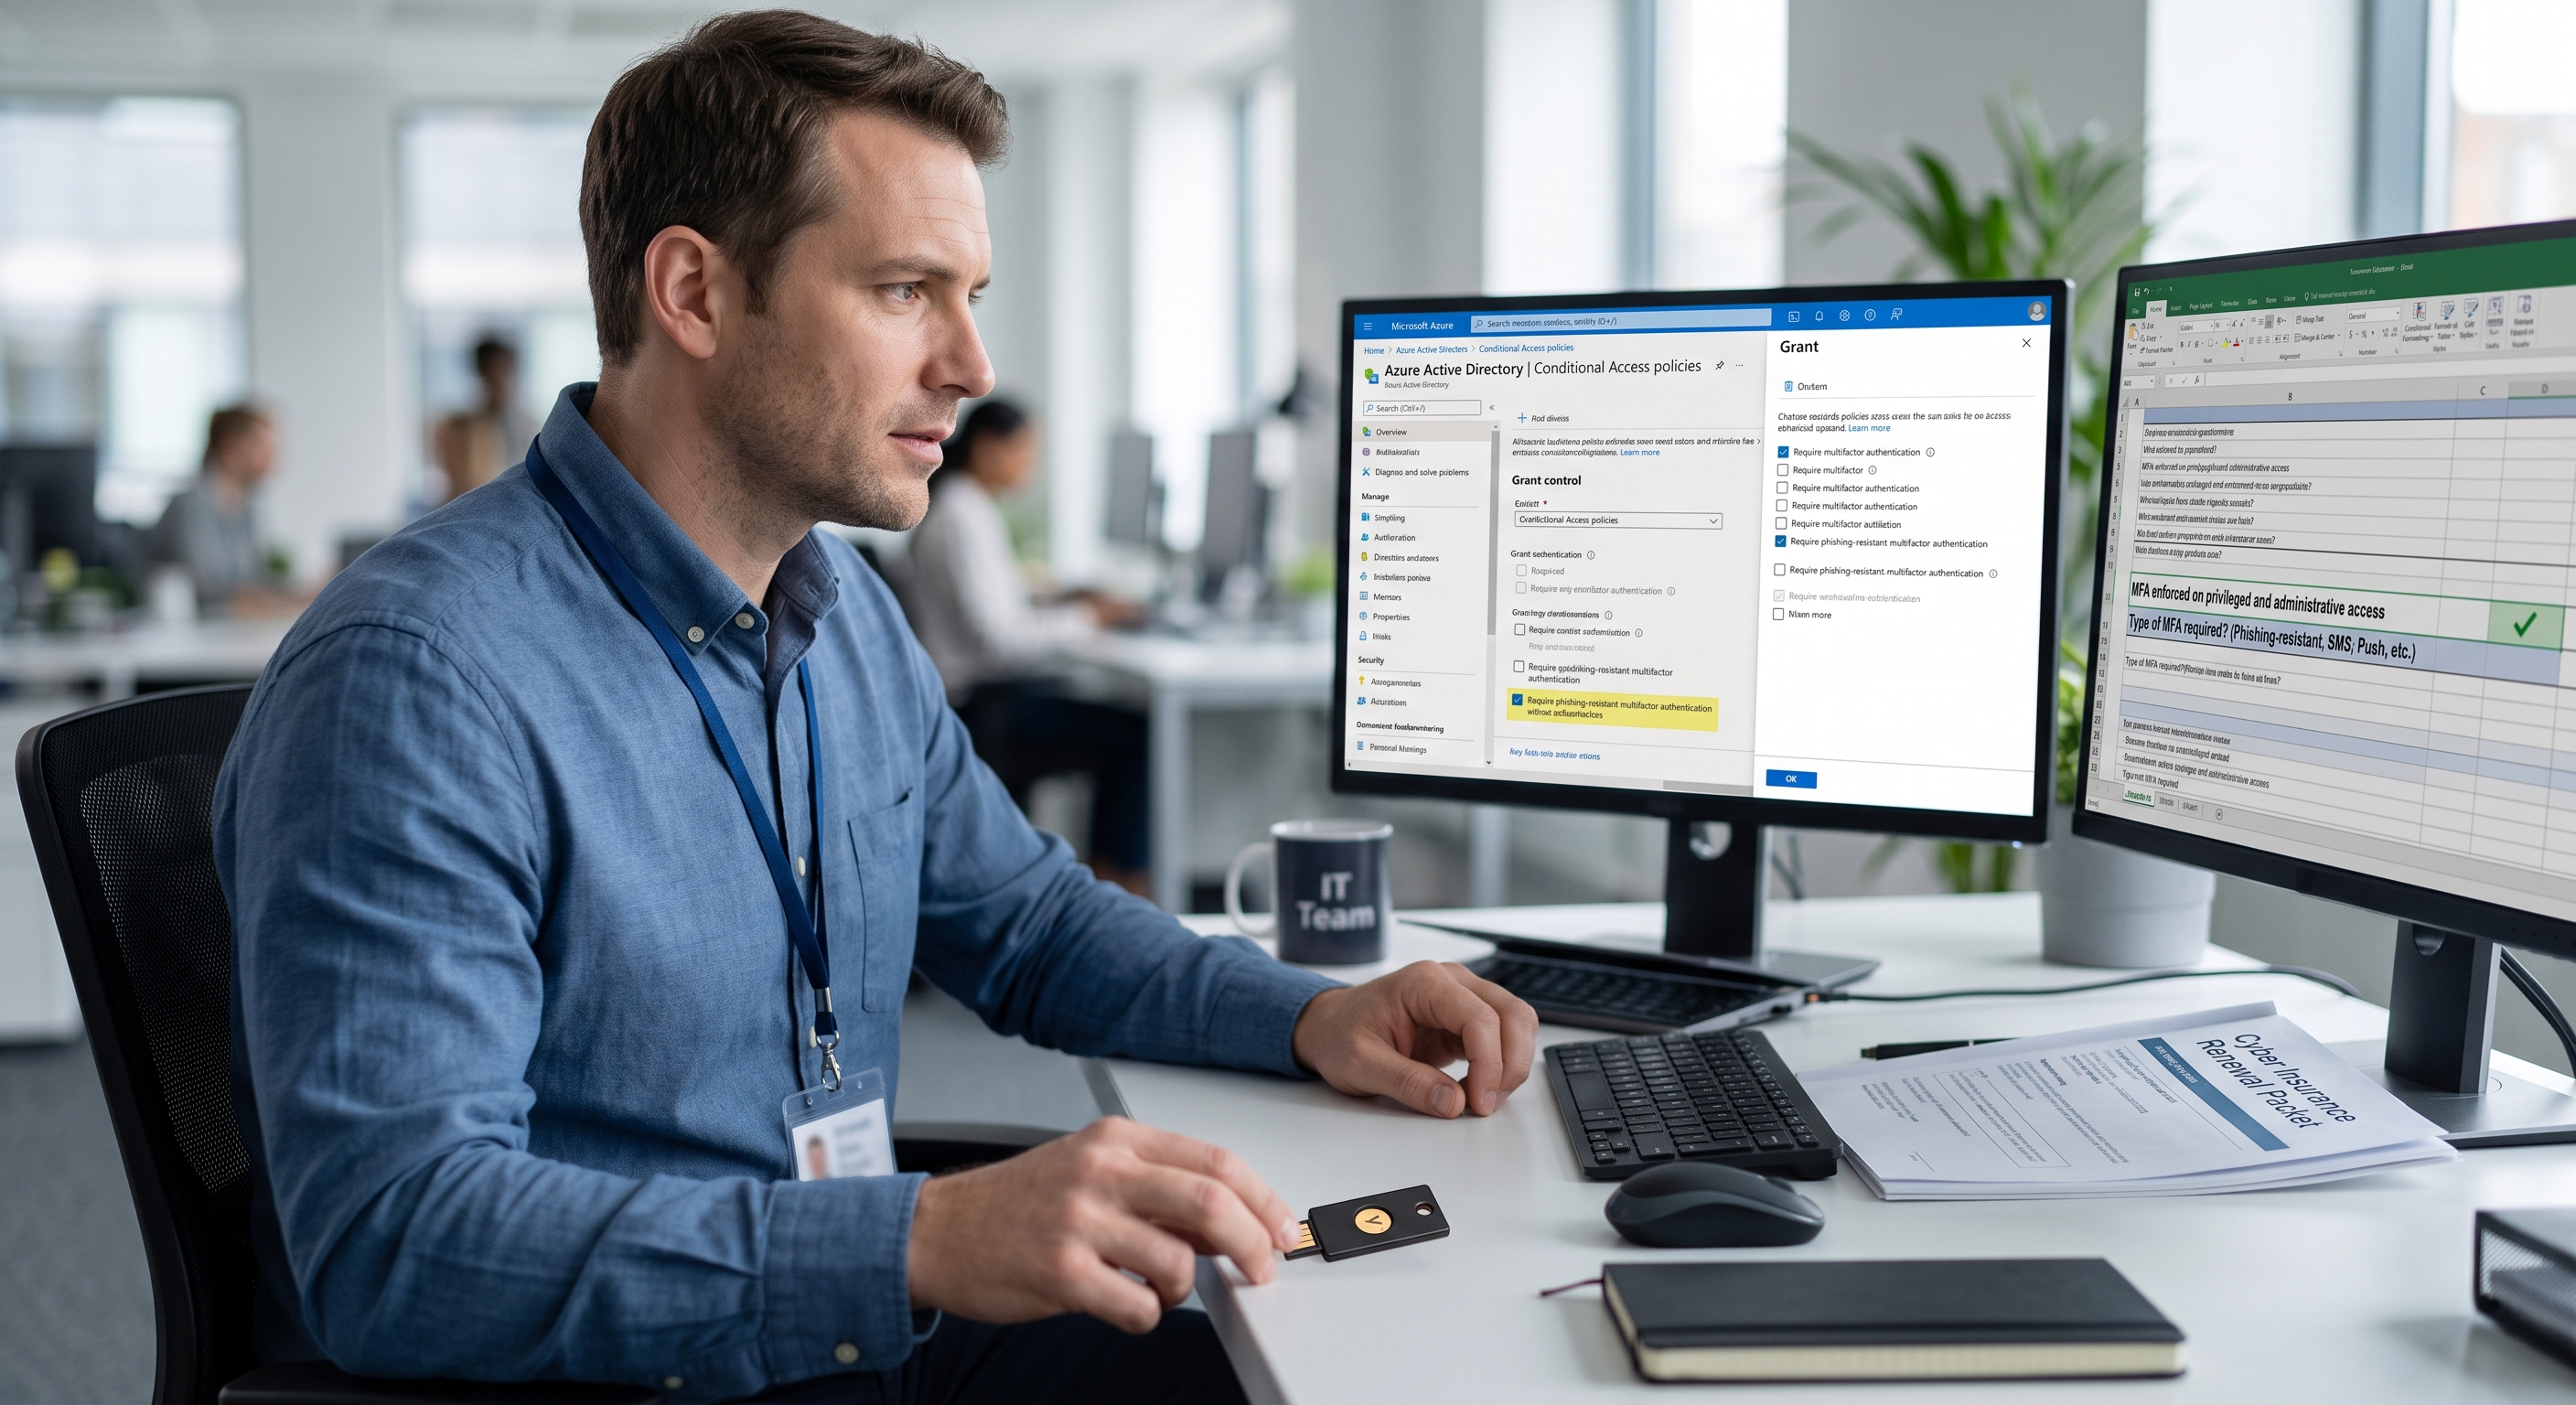
Somewhere in most cyber insurance renewal packets there's a line item that reads something like "MFA enforced on privileged and administrative access," and somewhere in most companies there's a security lead who checks that box without a second thought, because MFA has been turned on for years. The box gets checked. The renewal goes through. Nobody revisits it until a claim gets denied or a more detailed questionnaire arrives asking a sharper version of the same question - and the sharper version isn't asking whether MFA is on. It's asking which kind.
That distinction is where a lot of otherwise-careful security programs are quietly exposed, and it's easy to miss because both answers get described with the same three letters.
"MFA" Covers a Wide Range of Actual Security
A push notification a user taps to approve, a six-digit code texted to a phone, and a hardware security key that cryptographically proves possession of a physical device are all "multi-factor authentication." They are not remotely equivalent as a control. Push and SMS-based MFA are both vulnerable to real, common attack patterns - MFA fatigue attacks that spam approval prompts until someone taps yes out of habit or annoyance, and SIM-swap attacks that redirect the SMS code to an attacker's device entirely. Phishing-resistant MFA - FIDO2 hardware keys or certificate-based authentication, generally grouped under WebAuthn - doesn't have an equivalent bypass, because there's no code or approval prompt for an attacker to intercept or fatigue their way past.
Underwriters have caught up to this distinction faster than most internal security reviews have. A carrier questionnaire that used to ask "is MFA enforced?" is now more likely to ask specifically about phishing-resistant MFA on privileged and administrative accounts, and increasingly explicit that SMS and push no longer satisfy that line for higher-tier coverage. Coalition's own claims analysis has pointed to improperly implemented MFA as a factor in a large share of denied claims - not absent MFA, improperly implemented MFA, which is exactly the push/SMS gap described above.
Check This Against Your Own Policy, Not Your Own Memory
The question worth asking isn't "do we have MFA on privileged accounts" - almost everyone answers yes to that from memory. The question is: what does the Conditional Access policy governing those accounts actually require as the satisfying method, checked in the policy itself, right now? If it lists any authentication method, or explicitly allows SMS or push alongside FIDO2, that policy is satisfied by the weakest method in the list, not the strongest one available. A privileged account protected by a policy that permits a hardware key but doesn't require one is, in practice, protected by whatever the user chose to set up - which is usually whichever method was easiest to enable.
Where a PAM Platform's Job Actually Ends
This matters directly to how PAM-Pro's MFA control works, and I'd rather describe the boundary precisely than let the acronym do the talking. PAM-Pro verifies that a session authenticated with MFA before releasing a privileged credential - it reads the token's amr claim and refuses the checkout outright if MFA isn't asserted, with the refusal logged. What it does not do is request a specific authentication method or evaluate which one satisfied the challenge. Enforcement of MFA generally, and the choice of which methods count as satisfying it, both live entirely in the policyholder's own Conditional Access policy - not in PAM-Pro, and not in any PAM platform sitting downstream of Entra ID the same way.
That's not a gap in the product so much as an accurate description of where the responsibility actually sits. Deploying PAM tooling correctly answers "is access governed and logged." It does not, by itself, answer "is the MFA protecting that access phishing-resistant" - that second question gets answered by the Conditional Access policy alone, and it's worth going and checking it directly rather than assuming the first yes covers the second question too. The full control-by-control breakdown, including where this is marked a shared control rather than a fully satisfied one, is in the Underwriting Impact Overview.
© 2026 Huntoso LLC. All rights reserved.